By hitmind.ai | Published 2026-10-08 | Updated 2026-10-08
Enterprise GSC service account permissions management best practices require more than choosing a Search Console role. Secure access is the intersection of the GSC property permission, the OAuth scope, and the credential execution path. Keep each service account single-purpose, default reporting workloads to read-only access, and reserve write permissions for isolated jobs.
This guide provides a practical control model for SaaS teams operating Search Console data pipelines across multiple sites, business units, or client properties.
What permissions does a GSC service account actually need?
A GSC service account needs permission at two separate authorization layers. First, its email address must be added to the relevant Search Console property. Second, its access token must request an OAuth scope allowed by the API method.
Google Search Console defines Owner, Full user, and Restricted user roles. Owners control users and settings; Full users can view all data and perform selected actions; Restricted users receive simpler view access. Google recommends granting only the level required and regularly auditing property access. (support.google.com)
The API separately defines two scopes:
webmasters.readonlyfor read-only accesswebmastersfor read/write access
Granting a broad OAuth scope does not override a narrow property role. Likewise, making an account a GSC Owner does not eliminate the need for the correct API scope. (developers.google.com)
How should enterprises apply the three-lock permission model?
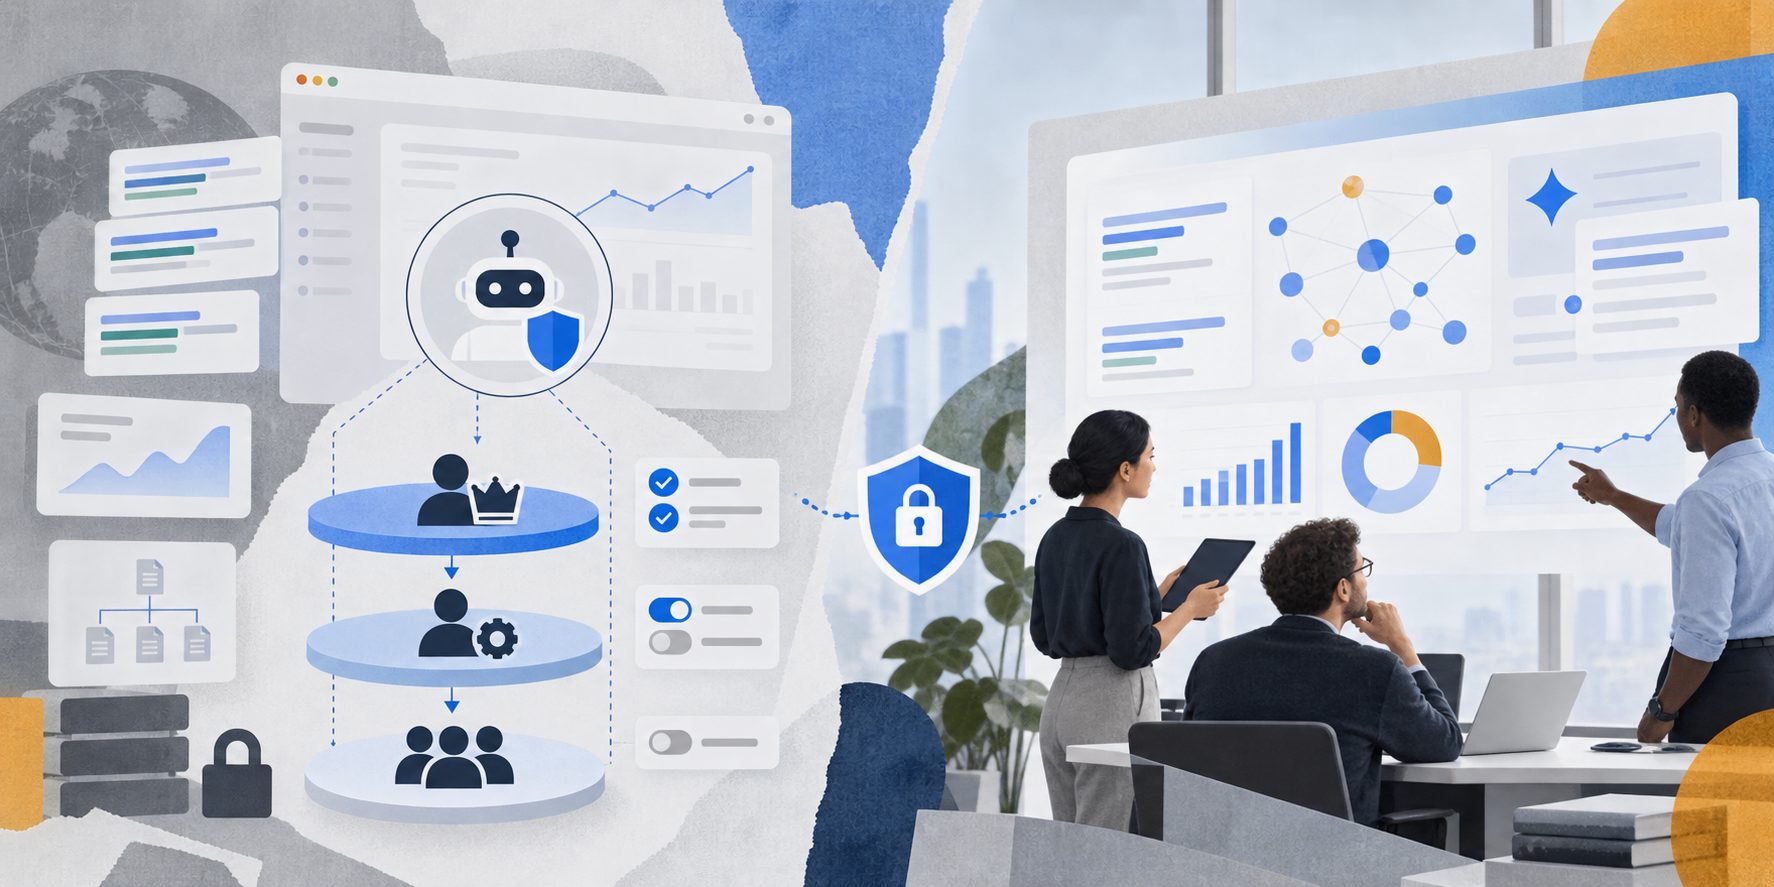
The three-lock model treats authorization as an intersection, not a single role. A request succeeds only when the GSC property role, OAuth scope, and runtime identity all permit the action. This prevents teams from treating “service account access” as one oversized permission.
Lock 1: Search Console property access
Add the service account only to properties its workload must process. Do not grant portfolio-wide access merely because centralized reporting may need it later.
Lock 2: OAuth scope
Use webmasters.readonly for performance reports, property discovery, and index-status retrieval. The Search Analytics query and URL Inspection endpoints both accept the read-only scope. Sitemap submission requires the read/write webmasters scope. (developers.google.com)
Lock 3: Credential execution
Control which workload can impersonate or authenticate as the account. Google recommends avoiding downloadable service account keys where a safer method—such as an attached identity, impersonation, or Workload Identity Federation—is available. (docs.cloud.google.com)
Which role and scope fit each GSC workload?
The following original permission-envelope analysis maps four common enterprise workflows across three authorization controls. The method compares Google’s documented API scopes with Search Console’s documented action permissions, producing 12 explicit access decisions rather than one generic “GSC access” grant.
| Workload | Starting GSC role | OAuth scope | Credential pattern |
|---|---|---|---|
| Daily Search Analytics export | Restricted user | webmasters.readonly |
Keyless workload identity |
| URL Inspection monitoring | Restricted user | webmasters.readonly |
Separate read-only account |
Property inventory with sites.list |
Restricted user | webmasters.readonly |
Central inventory account |
| Sitemap submission | Full user | webmasters |
Isolated write-enabled account |
Restricted access is the appropriate starting point for read-only automation because Restricted users can view Performance data and fetch URL Inspection results. Validate the exact endpoint against a staging property before production rollout, since the effective permission is determined by all three locks. (support.google.com)
A sitemap job should not share credentials with a reporting pipeline. Full users can submit sitemaps, while Restricted users cannot, and the API method requires the write-enabled scope. (support.google.com)
For extraction implementation details, see the workflows for exporting all Search Console queries and building a reliable GSC-to-BigQuery sync.
How do you deploy GSC service accounts securely?
A secure deployment separates reporting, write operations, and administration into different identities. This limits the blast radius of a compromised workload and creates logs that identify which system performed an action.
- Define one business purpose. Document the application owner, data owner, approved properties, endpoints, environment, and removal date.
- Create a single-purpose account. Do not reuse the reporting identity for sitemap changes, experiments, or unrelated Google APIs.
- Grant property-level access. Add the service account email only to approved GSC properties.
- Select the narrowest scope. Start with
webmasters.readonly; add write access only when an endpoint requires it. - Prefer keyless authentication. Use attached service accounts or Workload Identity Federation where the runtime supports them.
- Run positive and negative tests. Confirm the required endpoint works and an intentionally prohibited operation fails.
- Record the approved envelope. Store the property list, role, scope, workload identity, and review date in the access register.
For production reliability, monitor failed authorization requests separately from quota failures. A 403 caused by property access should not be handled like API throttling. This GSC API rate-limit monitoring workflow explains the quota side of that distinction.
What controls are required when JSON keys cannot be avoided?
Long-lived JSON keys should be an exception with a named owner and expiration plan. Anyone possessing a service account key can authenticate as that identity, so the key must be protected as carefully as the Search Console data it exposes.
If a legacy platform requires a JSON key:
- Store it in a controlled credential system, never in source code.
- Block downloads to unmanaged workstations.
- Restrict access to the production workload identity and designated security administrators.
- Rotate the key through a tested overlap procedure.
- Alert on unexpected key creation and authentication locations.
- Revoke the key immediately when the integration is retired.
- Prohibit domain-wide delegation unless a separately reviewed use case requires it.
Google notes that downloaded keys do not expire by default and recommends routine rotation. It also advises reducing the number of keys in circulation and disabling key creation where keys are unnecessary. (docs.cloud.google.com)
How should GSC access be reviewed and offboarded?
Review each service account as a workload, not merely as an email address. The reviewer must confirm that the application still exists, its property list is current, its scope remains necessary, and its credential path has an accountable owner.
Run reviews quarterly for production automation and immediately after an application, agency relationship, domain portfolio, or team owner changes. The review should answer:
- Did the account authenticate during the review period?
- Are all connected properties still in scope?
- Can a Restricted role replace Full access?
- Can
webmasters.readonlyreplacewebmasters? - Are active keys documented and rotated?
- Does disabling the account trigger a monitored failure?
- Is an owner responsible for approving continued access?
Offboarding requires removing the account from Search Console properties and disabling its authentication path. Removing only the JSON key leaves property access assigned; removing only the property role leaves a reusable credential. For verified human owners, Google also warns that leftover verification tokens must be removed to prevent re-verification. (developers.google.com)
Common questions
Should a GSC service account be an Owner?
Usually not. Routine reporting, URL inspection, and sitemap automation do not require user administration. Owner access should remain with a small number of accountable human administrators because Owners can manage users, settings, data, and tools. (support.google.com)
Is a Google Cloud IAM role enough to access Search Console?
No. The service account must also be granted access to the specific Search Console property. Google Cloud IAM controls who can use or manage the service account; GSC property permissions control what that identity can access in Search Console.
Can one service account cover every company website?
It can, but it generally should not. Segment accounts by environment, business boundary, and function. A compromise of one shared identity would otherwise expose every property assigned to it.
What is the safest default configuration?
For most reporting pipelines, start with a single-purpose service account, Restricted property access, the webmasters.readonly scope, keyless authentication, explicit property allowlists, and quarterly access reviews. Elevate only the layer required by a documented operation.
Final checklist
Enterprise GSC service account permissions management best practices can be reduced to one rule: minimize the permission envelope, not just the visible GSC role. Separate read and write workloads, avoid Owner access for automation, prefer short-lived keyless credentials, test denied operations, and remove both property access and credentials during offboarding.